As applications become increasingly interconnected and dependent on third-party software, developers play a critical role in reducing security risk. GLS' Secure Coding with the OWASP Top 10 training helps developers understand today's most important application security risks and make better security decisions throughout the software development lifecycle.
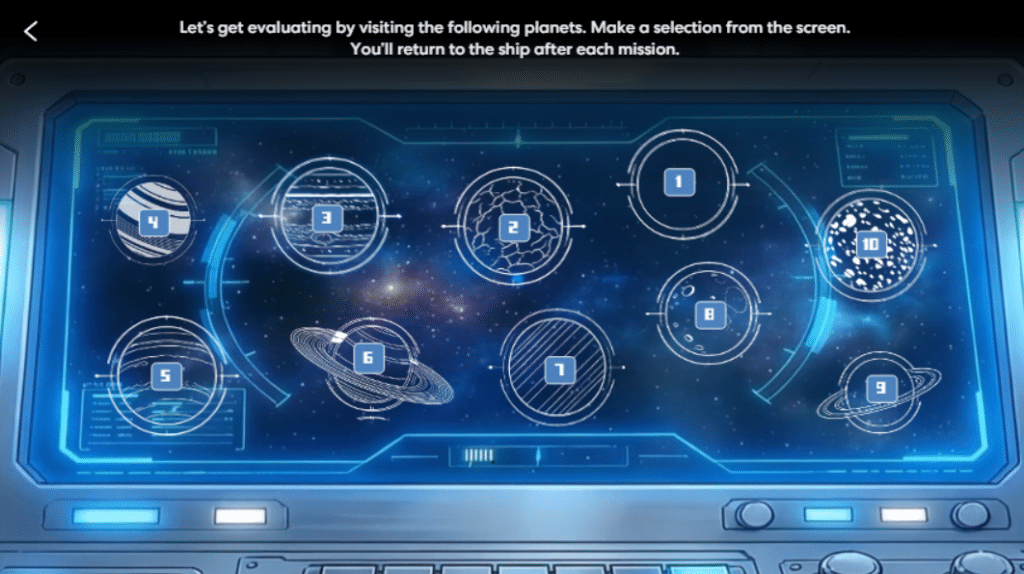
Based on the latest changes made to the OWASP Top 10, this training explores the key vulnerabilities identified by OWASP as the most significant risks facing modern applications. During this mission-based learning experience, developers will investigate incidents, make decisions, evaluate consequences, identify root causes, and explore remediation strategies to keep their development environments secure.
Topic
Secure Coding (OWASP Top 10)
Learning Modality
Interactive Modules
Role/Audience
Developers
Language
English Only
Total Time
90 Minutes
Course Features:
Interactive mission-based learning
Realistic scenarios and modern attack paths
Decision-driven exercises with meaningful consequences
Language-agnostic content
Practical security awareness for everyday development decisions
Course Curriculum:
Module 1: Broken Access Control
Module 2: Security Misconfiguration
Module 3: Software Supply Chain Failures
Module 4: Cryptographic Failures
Module 5: Injection
Module 6: Insecure Design
Module 7: Authentication Failures
Module 8: Software or Data Integrity Failures
Module 9: Security Logging and Alerting Failures
Module 10: Mishandling of Exceptional Conditions
Learning Objectives:
Recognize common security risks identified in OWASP Top 10: 2025
Understand how security weaknesses emerge in modern systems
Identify vulnerabilities across application environments
Evaluate how security controls fail or are bypassed
Apply security awareness to everyday development decisions
Want to learn more GLS' Secure Coding training?
Please complete the form below and a GLS representative will contact you.